> ## Documentation Index
> Fetch the complete documentation index at: https://docs.dqlabs.ai/llms.txt
> Use this file to discover all available pages before exploring further.
# Azure Active Directory/Entra ID
> Step-by-step guide to configuring Microsoft Entra ID (Azure AD) as the SAML 2.0 identity provider for single sign-on into Prizm.
### Overview
This guide describes how to configure **Microsoft Entra ID (formerly Azure Active Directory)** as the SAML 2.0 Identity Provider (IdP) for PRIZM. After completing the configuration, users assigned to the PRIZM Enterprise Application can securely authenticate using their Microsoft Entra ID credentials.
## Prerequisites
Before you begin, ensure you have:
* Microsoft Entra ID Administrator privileges
* Permission to create Enterprise Applications
* Permission to configure SAML Single Sign-On
* PRIZM Administrator access
* PRIZM Service Provider (SP) details:
* Entity ID
* ACS URL
* Sign-on URL
## Step 1: Configure Microsoft Entra ID
1. Sign in to the **Microsoft Entra Admin Center**.
2. Navigate to: **Enterprise Applications → New Application**
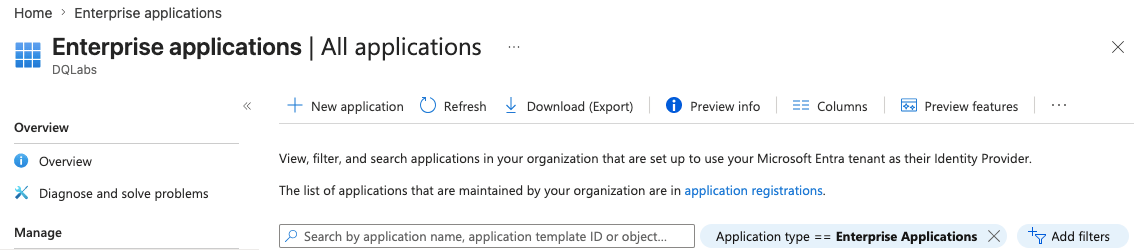 3. Select **Create your own application**.
4. Name the application **PRIZM**.
5. Choose **Integrate any other application you don't find in the gallery (Non-gallery)**.
6. Open the newly created application.
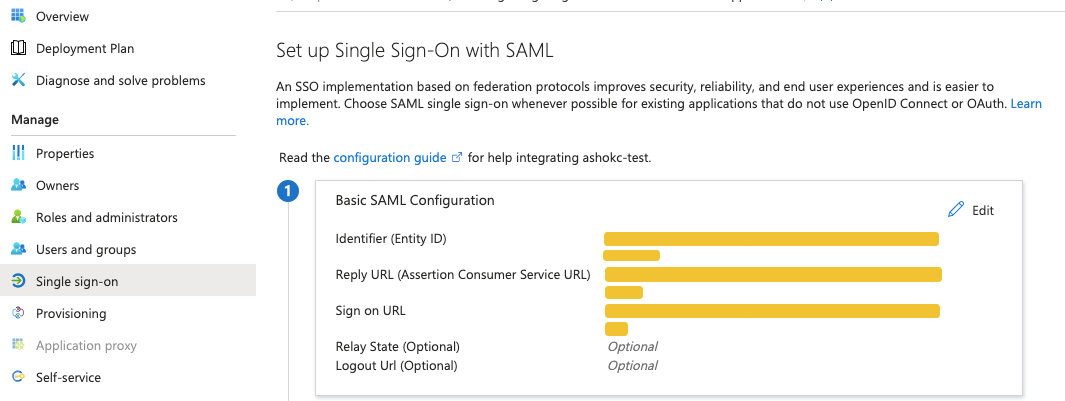
7. Navigate to: **Manage → Single Sign-On → SAML**
8. Configure the following values using the information available in **PRIZM → Profile → Organization → SSO/SAML**.
| Microsoft Entra ID Field | PRIZM Value |
| :----------------------- | :---------- |
| Identifier (Entity ID) | Entity ID |
| Reply URL (ACS URL) | ACS URL |
| Sign-on URL | Sign-on URL |
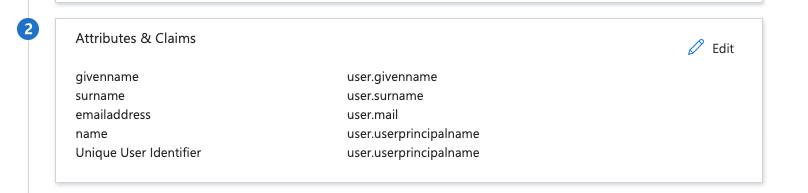
 9. Configure the required SAML claims.
| PRIZM Attribute | Microsoft Entra ID Attribute |
| :------------------ | :--------------------------- |
| emailaddress | user.mail |
| givenname | user.givenname |
| surname | user.surname |
| groups *(optional)* | Groups |
10. Save the configuration.
 ## Step 2: Configure PRIZM
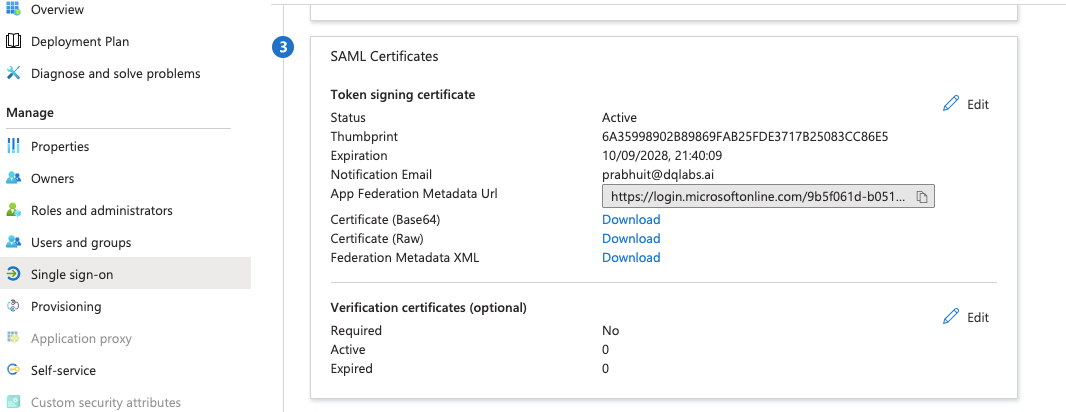
1. In Microsoft Entra ID, navigate to the **SAML Certificates** section.
2. Download the **Federation Metadata XML**.
 3. In PRIZM, navigate to: **Profile → Organization → SSO/SAML**
4. Enable **Single Sign-On**.
5. Select **Microsoft Entra ID** as the Identity Provider.
6. Upload the **Federation Metadata XML**.
7. Click **Save**.
## Step 3: Assign Users
In Microsoft Entra ID:
* Open the PRIZM Enterprise Application.
* Navigate to **Users and Groups**.
* Assign the required users or groups.
Users must be assigned before testing SSO.
## Step 4: Test Login
1. Navigate to the PRIZM login page.
2. Select **Sign in with SSO**.
3. Enter your corporate email address.
4. Authenticate using Microsoft Entra ID.
After successful authentication:
* Existing PRIZM users are authenticated.
* New users are automatically provisioned during their first login (JIT provisioning).
* Roles are assigned automatically based on incoming group mappings.
### SCIM Provisioning (Optional)
1. Navigate to **Enterprise Applications → PRIZM → Provisioning**.
2. Select **Automatic** provisioning.
3. Enter:
* Tenant URL (SCIM URL)
* Secret Token
4. Click **Test Connection**.
5. Configure attribute mappings.
6. Start provisioning.
7. Assign users/groups.