
Overview
Prizm offers comprehensive Single Sign-On (SSO) support, integrating with major identity providers to enable seamless authentication experiences while maintaining enterprise security standards. SSO eliminates password fatigue for users and centralizes identity governance for administrators.Supported Protocols
SAML 2.0 Integration
Service Provider Metadata
Use the following Prizm (Service Provider) values when configuring your identity provider:Configure SSO in Prizm
Open Organization → Security. The SSO Provider Configuration form contains:- Enabled — turns SSO on for the organization
- Select SSO Provider — the identity provider type, for example Azure Active Directory
- Override unique identifier — see Overriding the Unique Identifier
- Entity ID, Sign In URL, and ACS URL — the Prizm values to register with your identity provider; replace
<your-prizm-host>above with your instance host - SCIM URL and Group provisioning — the SCIM endpoint and a toggle for group provisioning (see SCIM)
- Federation File — upload the IdP federation metadata XML (maximum 5 MB)
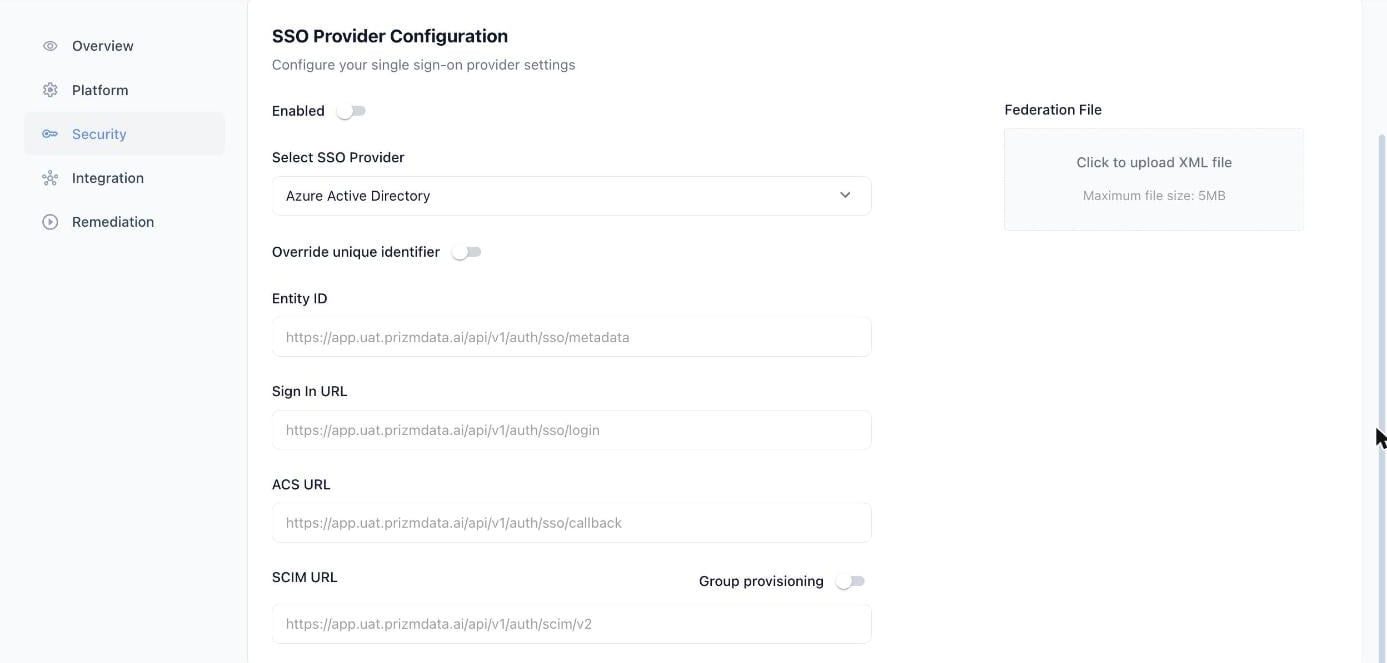
Organization → Security → SSO Provider Configuration
Required Attribute Assertions
Overriding the Unique Identifier
By default, Prizm matches SSO logins to Prizm accounts using the Email Address attribute from the SAML assertion — consistent with the Service Provider’s Name ID Format (emailAddress) above. Some organizations need a different, permanent attribute instead, since a user’s email can change over time (e.g., after a name change) while an internal identifier stays constant.
To use a permanent identifier instead of email:
1
Open Security settings
Navigate to Organization → Security.
2
Enable the override
Toggle Override unique identifier on. A confirmation prompt appears, warning that email will no longer be used as the unique identifier — confirm to proceed.
3
Set the identifier attribute
A new Unique identifier field appears, pre-filled with a provider-specific default (e.g.
object_id for Okta). Enter the name of the SAML attribute/claim your IdP sends that contains the permanent, immutable identifier for the user.4
Save
Click Save Configuration to apply the change.
Provider Setup
OAuth 2.0 / OpenID Connect
Configuration Steps
1
Register Prizm
Register Prizm as an OAuth 2.0 client application with your identity provider.
2
Note credentials
Note the Client ID and Client Secret provided by the IdP.
3
Set redirect URI
Configure the redirect URI:
https://app.prizm.io/auth/callback4
Configure in Prizm
Enter the Client ID, Client Secret, and discovery endpoint URL under Organization → Security.
5
Configure scopes
Confirm the required scopes are enabled:
openid, profile, email, groups.6
Test
Test the integration using the built-in Test SSO Connection button.
Required Scopes
Group Synchronization
Prizm automatically synchronizes group memberships from the identity provider, enabling automatic RBAC assignment based on IdP groups. This allows organizations to manage Prizm access through their existing directory management workflows.- IdP groups are synchronized at login and on configurable intervals
- Group membership changes in the IdP take effect on the user’s next login
- Multiple IdP groups can be mapped to a single Prizm role
- Role precedence rules apply when a user belongs to multiple mapped groups
Session Management
Security Considerations
All SAML assertions must be signed by the IdP. Prizm validates assertion signatures using the configured IdP certificate. Certificate rotation is supported without service interruption.
- Failed authentication attempts are logged in the audit trail
- JIT (Just-in-Time) user provisioning creates accounts on first SSO login
- Deprovisioned IdP accounts lose Prizm access on next session validation