
How it works
- Prizm exposes a SCIM URL visible under Organization → Security.
- You configure your IdP to send provisioning requests to that URL using a bearer token for authentication.
- Whenever a user is added, changed, or removed in your IdP, it pushes a SCIM request to Prizm.
- Prizm applies the change — creating the account, updating the profile, or deactivating access.
Supported providers
IBM Security Verify supports user provisioning only. Group synchronization is not available for IBM. Use Okta, Azure AD, or Ping Identity if group-based access management is required.
What SCIM manages
Prerequisites
- SAML SSO must already be configured in Prizm for your IdP before enabling SCIM.
- You need admin access to both Prizm (Organization → Security) and your IdP.
- A static bearer token is required for the IdP to authenticate to Prizm’s SCIM endpoint.
If your organization uses Override unique identifier (under Organization → Security) to match SAML logins by a permanent attribute instead of email, configure the matching SCIM field below with that same attribute, so SCIM-provisioned accounts resolve to the same identity as SAML logins. See SSO Integration Overview for details, and Unique identifier and externalId below for the SCIM field to use.
Finding the SCIM URL
- In Prizm, navigate to Organization → Security.
- Locate the SCIM URL field (read-only).
- Copy this URL — paste it into your IdP’s SCIM provisioning configuration as the SCIM Base URL or Tenant URL.
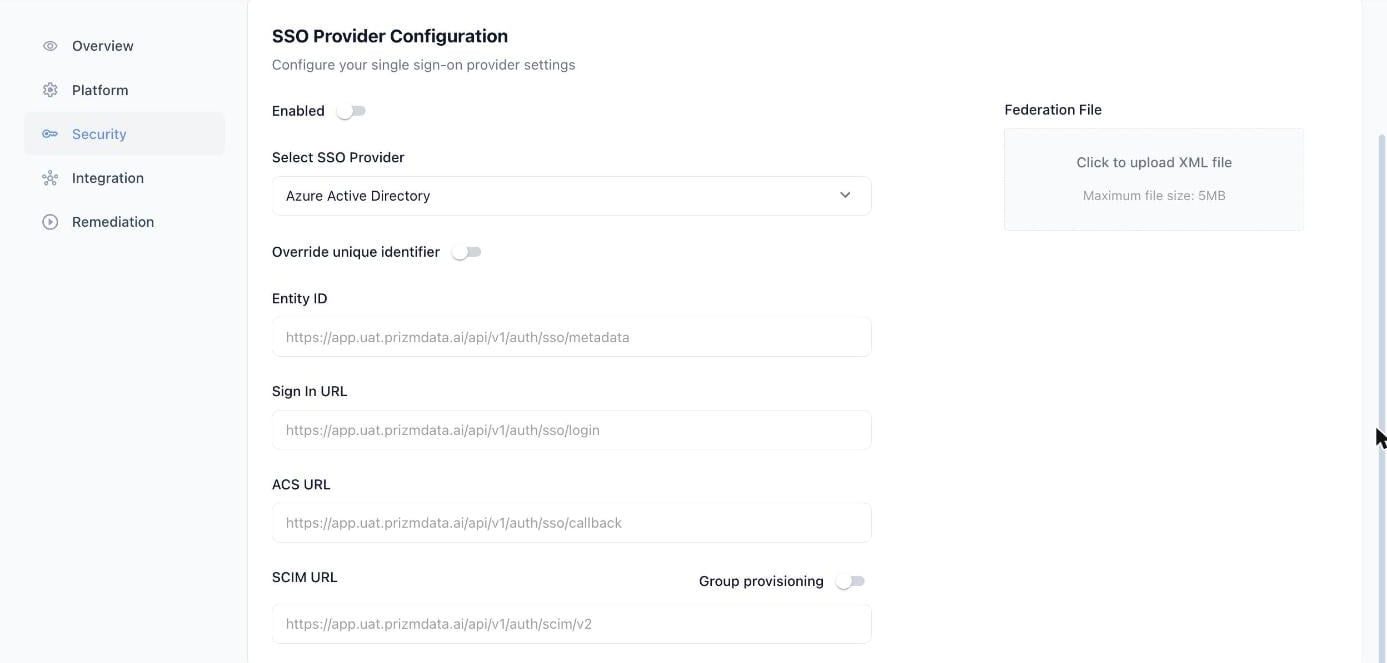
Organization → Security: SSO Provider Configuration, including the SCIM URL
Setup by provider
- Okta
- Azure AD / Entra ID
- Ping Identity
- IBM Security Verify
Prerequisites
- Okta SAML SSO is already configured for Prizm.
- You have Okta Administrator access.
- You have the Prizm SCIM URL.
Step 1 — Open SCIM provisioning in Okta
- In the Okta Admin Console, navigate to Applications and open the Prizm SAML application.
- Go to the Provisioning tab → Integration section.
- Click Configure API Integration and enable API Integration.
Step 2 — Configure the SCIM endpoint
Click Test API Credentials to verify the connection, then Save.
Step 3 — Enable provisioning to app
Under Provisioning → To App, enable:Step 4 — Map attributes
Step 5 — Push groups (optional)
- Go to the Push Groups tab in the Provisioning section.
- Click Push Groups and search for the Okta groups to sync.
- Select the groups and click Save.
SCIM endpoints
All IdPs use the same Prizm SCIM endpoints:IBM Security Verify does not call the Groups endpoints. Group endpoints are used by Okta, Azure AD, and Ping Identity only.
Unique identifier and externalId
By default, Prizm matches users by email address. If your organization uses Override unique identifier to match users by a permanent attribute instead, SCIM must also supply that attribute’s value for every user. SCIM stores it in the user’sexternalId field. When the value in externalId matches the value your identity provider (IdP) sends at login, SCIM-provisioned accounts and SSO logins resolve to the same Prizm user.
This section walks through the setup from start to finish, using Microsoft Entra ID (Azure AD) as the example. The same approach applies to other IdPs.
How the pieces fit together
Three settings work together, and each holds a different thing:
The claim name lives in the Prizm UI only. The SCIM PATCH path is always
externalId, whichever claim you choose.
Before you begin
- SAML SSO is configured for your IdP, and SCIM provisioning is set up as described above.
- You have administrator access to Prizm and to your IdP.
- You have the SCIM URL and bearer token. Examples below use the full
/api/v1/auth/scim/v2path, and the base is the SCIM URL under Organization → Security.
Choose the identifier
Pick an attribute that is unique to each user and never changes. Prizm accepts the name of any claim your IdP sends. These are the common Azure claims:Set up the unique identifier
1
Send the claim from your IdP
Done by the IdP administrator.In Microsoft Entra ID, open the Prizm enterprise application and go to Manage → Single Sign-On → SAML. Add the claim you chose, for example
objectidentifier with source attribute user.objectid, and save. The claim must be part of the SAML assertion, because Prizm reads it at login.2
Configure Prizm
Done by the Prizm administrator.
- Navigate to Organization → Security.
- Turn on Override unique identifier and confirm the prompt.
- In the Unique identifier field, enter the claim name, for example
objectidentifier. - Click Update Configuration.
Prizm uses
externalId to look up users only while Override unique identifier is on. If it is off, Prizm does not use externalId for lookup, so turn it on before relying on externalId.3
Send the identifier value through SCIM
Done by whoever manages provisioning.Send each user’s identifier value in The value must be the same one your IdP sends in the selected claim for that user. For
externalId. Include it when you create a user, or update it on an existing one.- Existing user (PATCH)
- New user (POST)
objectidentifier, that is the user’s Azure Object ID.4
Verify the stored value
Retrieve the user and confirm If
externalId holds the expected value:externalId is still null, see Troubleshooting below.5
Test SSO login
Have the user sign in with SSO. Confirm they land on the same Prizm account that SCIM provisioned, which shows that the claim from the assertion and the SCIM identifier resolve to the same user.
6
Keep the identifier consistent
Use the same external identifier for every later SCIM create, update, and filter operation for that user.
Reference
SCIM fields
Find a user by external identifier
Recommended configuration
Troubleshooting the unique identifier
Example of an incorrect request
Example of an incorrect request
This PATCH uses an unsupported field. Replace
externalAttribute1 with externalId.