
Overview
This guide describes how to configure IBM Security Verify as the SAML 2.0 Identity Provider (IdP) for PRIZM. After completing the configuration, entitled users can securely authenticate to PRIZM using their IBM Security Verify credentials.Prerequisites
Before you begin, ensure you have:- IBM Security Verify Administrator privileges
- Permission to create SAML applications
- PRIZM Administrator access
- PRIZM Service Provider (SP) details:
- Entity ID
- ACS URL
- Sign-on URL
Step 1: Configure IBM Security Verify
- Sign in to the IBM Security Verify Admin Console create your tenant.
- Navigate to: Applications → Add Application
- Select Custom Application.
- Configure SAML 2.0 as the sign-on method and make sure “Use metadata” is disabled.
- Provide the application details (Application Name, Company Name, Owner) in General tab.
- Configure the following SAML settings using the values available in PRIZM → Profile → Organization → SSO/SAML.
- Configure the required attribute mappings.
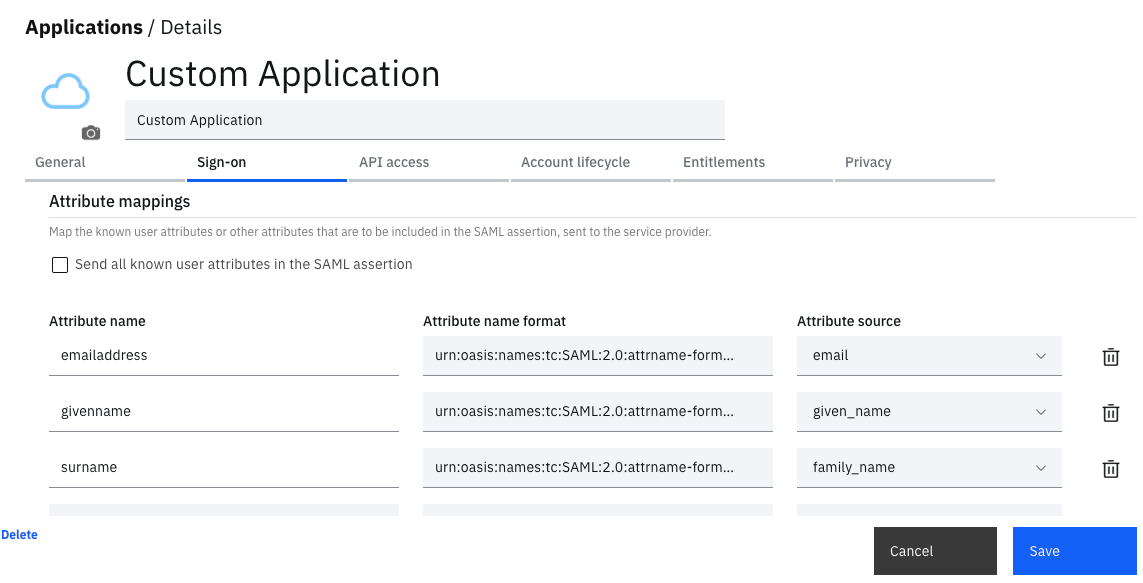
- Save the application.
Step 2: Configure PRIZM
- Download the Federation Metadata XML from IBM Security Verify.
IBM Security Verify does not provide a download button on the application page. The Federation Metadata XML is accessed via a direct tenant-level URL.- Open in browser: Paste the following URL into your browser while logged into IBM Security Verify:
https:///v1.0/saml/federations/saml20ip/metadata
- Save the file: Right-click the page → Save as → ensure the filename ends in .xml
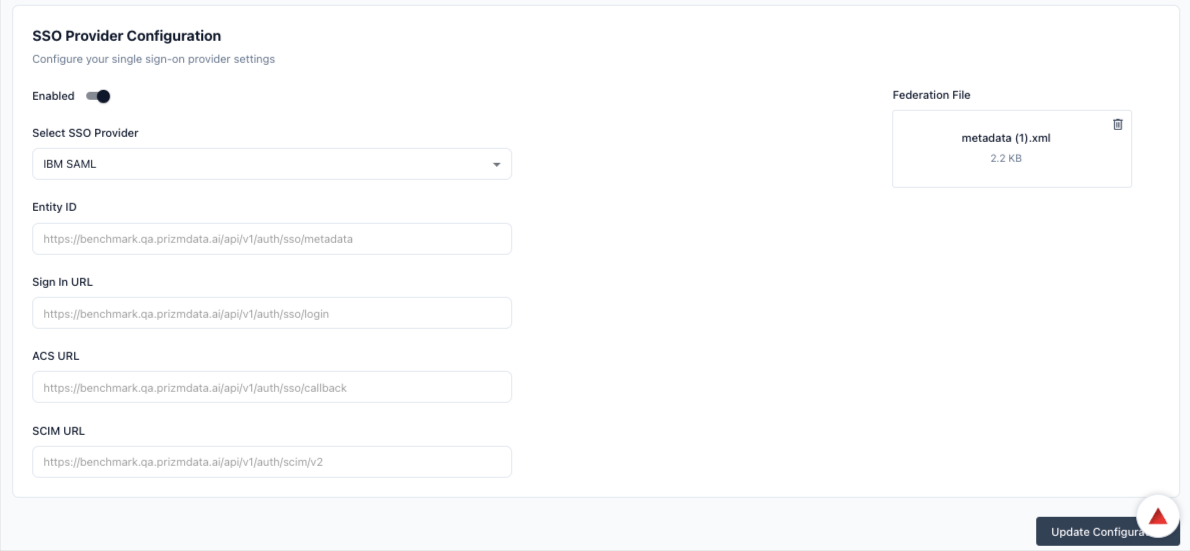
- In PRIZM, navigate to: Profile → Organization → SSO/SAML
- Enable Single Sign-On.
- Select IBM Security Verify as the Identity Provider.
- Upload the Federation Metadata XML.
- Click Save.
Step 3: Assign Users
In IBM Security Verify:- Open the PRIZM application.
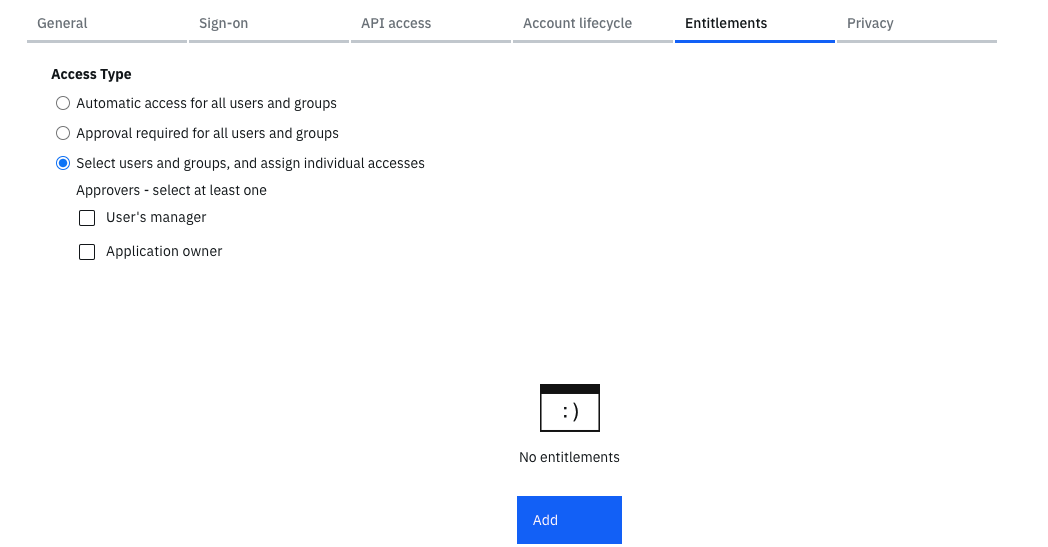
- Navigate to the Entitlement tab.
- Assign the required users or groups.
- Save the configuration.
Step 4: Test Login
- Navigate to the PRIZM login page.
- Select Sign in with SSO.
- Enter your corporate email address.
- Authenticate using IBM Security Verify.
- Existing PRIZM users are authenticated.
- New users are automatically provisioned during their first login (JIT provisioning).
- Roles are assigned automatically based on incoming group mappings.
SCIM Provisioning (Optional)
- Open the PRIZM application.
- Configure SCIM provisioning.
- Enter:
- SCIM Endpoint
- Authentication Token
- Save the configuration.
- Enable provisioning.
- Assign users/groups.