
Overview
This guide describes how to configure Ping Identity (PingFederate or PingOne) as the SAML 2.0 Identity Provider (IdP) for PRIZM.Prerequisites
Before you begin, ensure you have:- Ping Identity Administrator privileges
- Permission to create SAML applications
- PRIZM Administrator access
- PRIZM Service Provider (SP) details:
- Entity ID
- ACS URL
- Sign-on URL
Step 1: Configure Ping Identity
- Log in to the Ping Identity Admin Console.
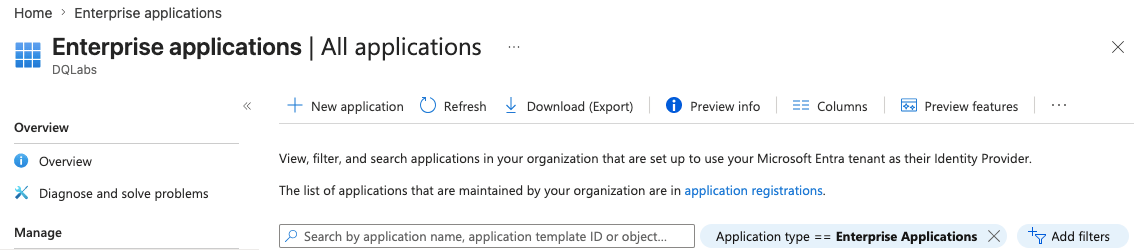
- Navigate to: Applications → Add Application
- Create a new SAML Application named PRIZM.
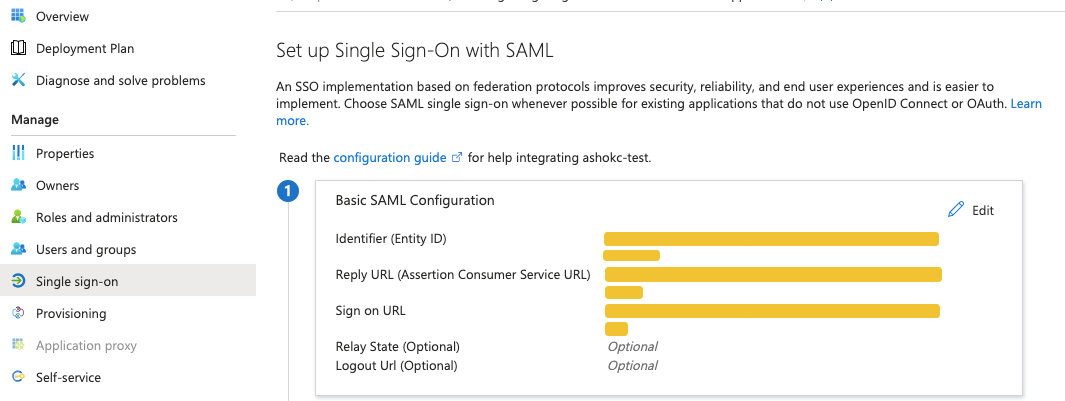
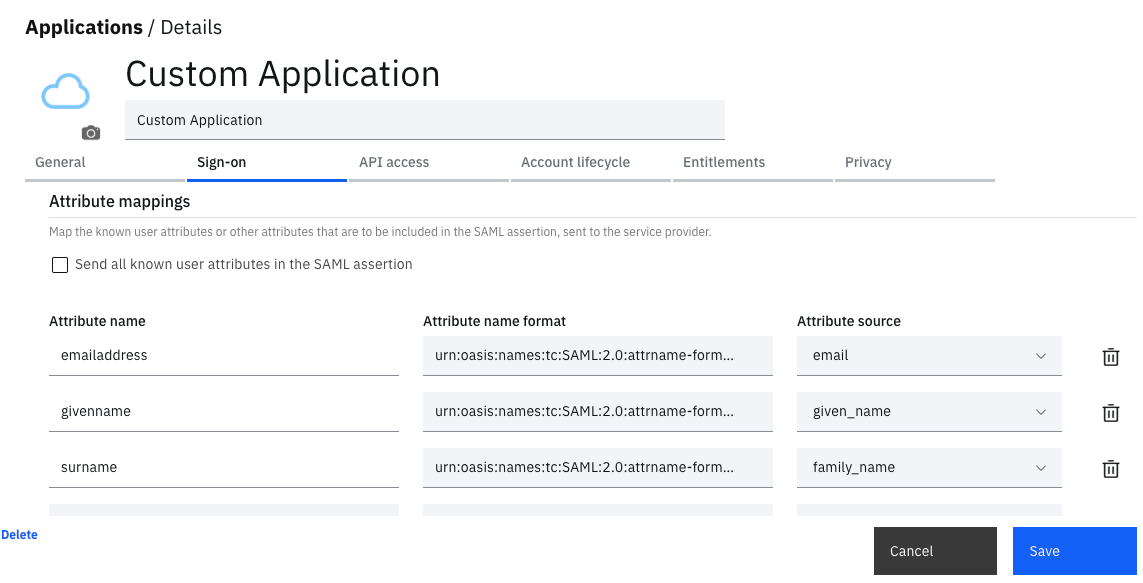
- Configure the application manually using the values available in PRIZM → Profile → Organization → SSO/SAML.
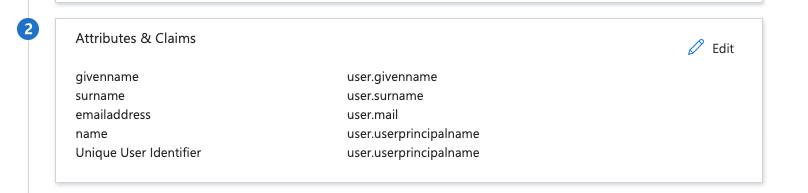
- Configure the required attribute mappings:
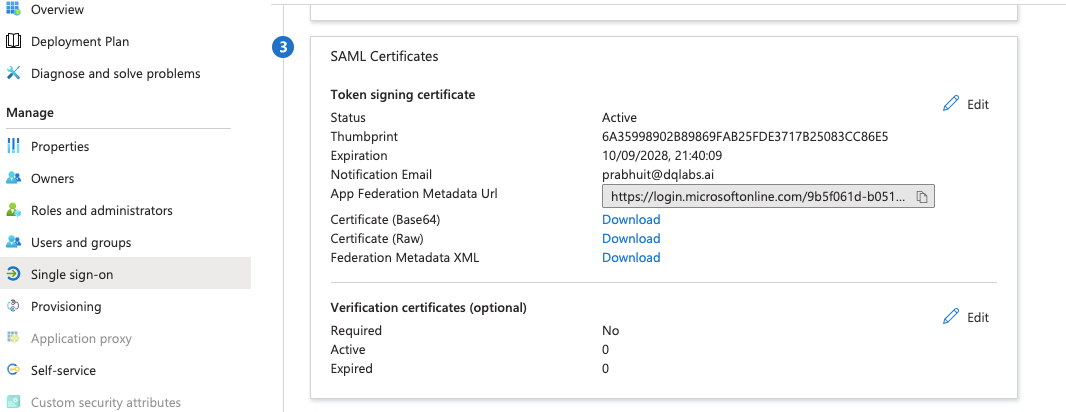
- Save the application and enable the toggle button at the top.
Step 2: Configure PRIZM
- Open the configured PRIZM application in Ping Identity.
- Download the Federation Metadata XML.
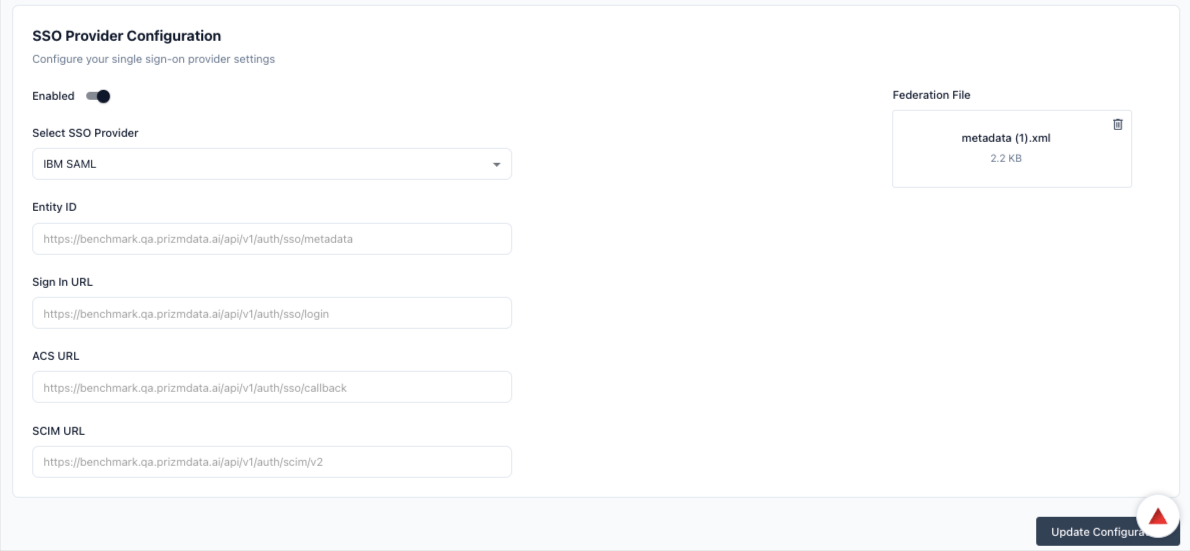
- In PRIZM, navigate to: Profile → Organization → SSO/SAML
- Enable Single Sign-On.
- Select Ping Identity.
- Upload the Federation Metadata XML.
- Click Save.
Step 3: Assign Users
In Ping Identity:- Open the PRIZM application and go to Access tab.
- Assign the required users or groups.
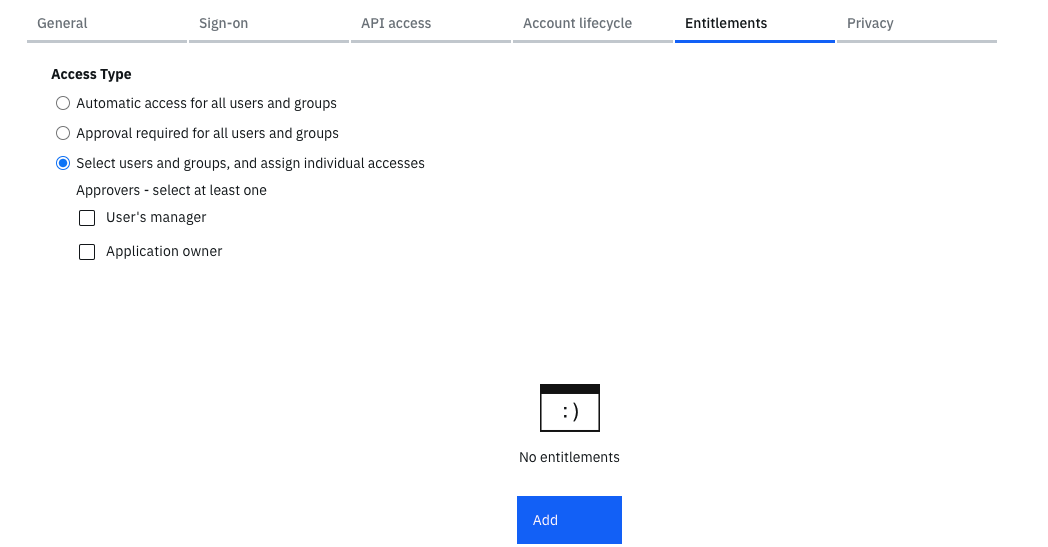
- Go to access page and enable SSO for the users
Step 4: Test Login
- Open the PRIZM login page.
- Select Sign in with SSO.
- Enter your corporate email address.
- Authenticate using Ping Identity.
- Existing PRIZM users are signed in.
- New users are automatically created during their first login (JIT provisioning).
- Roles are assigned automatically based on incoming group mappings.
SCIM Provisioning (Optional)
- Open the PRIZM application.
- Navigate to Provisioning / SCIM.
- Configure:
- SCIM Endpoint
- Bearer Token
- Save.
- Enable provisioning.
- Assign users/groups.